01No VPN
Direct internet
The GL.iNet uses whichever local internet connection is currently available. This can be hotel or apartment Wi-Fi, Ethernet, or another available connection. In this mode, traffic reaches the internet directly without a VPN.
In-house network project • VPN • redundancy
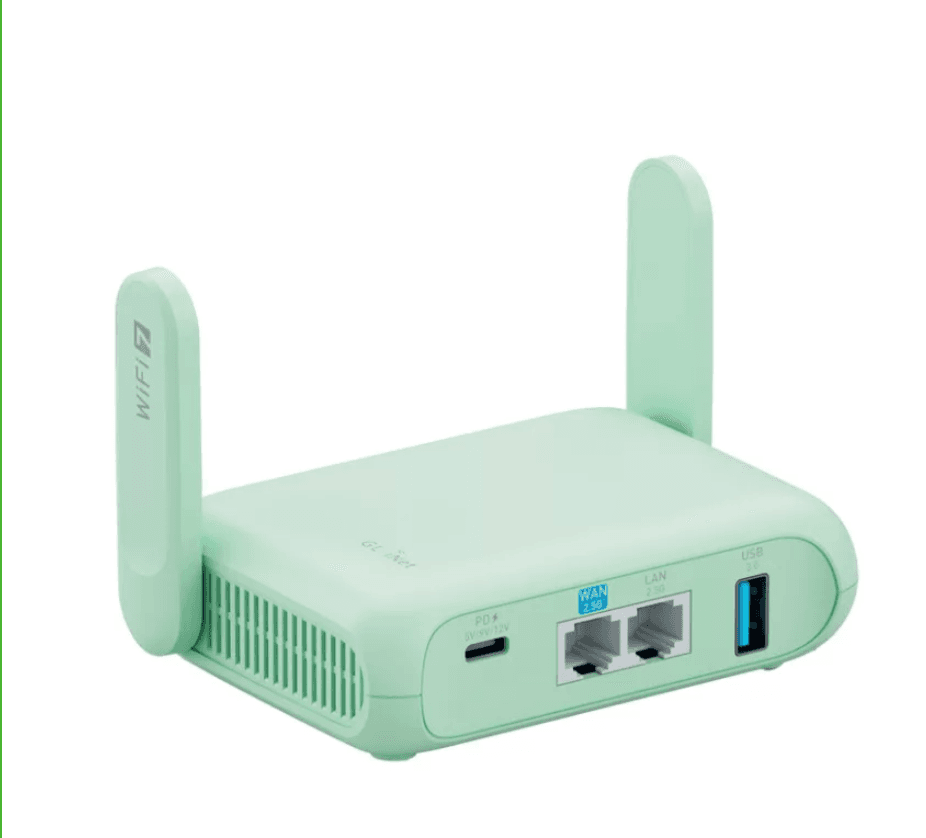
A GL.iNet GL-MT3600BE configured so the same private Wi-Fi network can use three completely different exit paths: direct local internet, a dedicated server-room OpenVPN endpoint, or WireGuard to a MikroTik endpoint with ONE and Telekom failover.
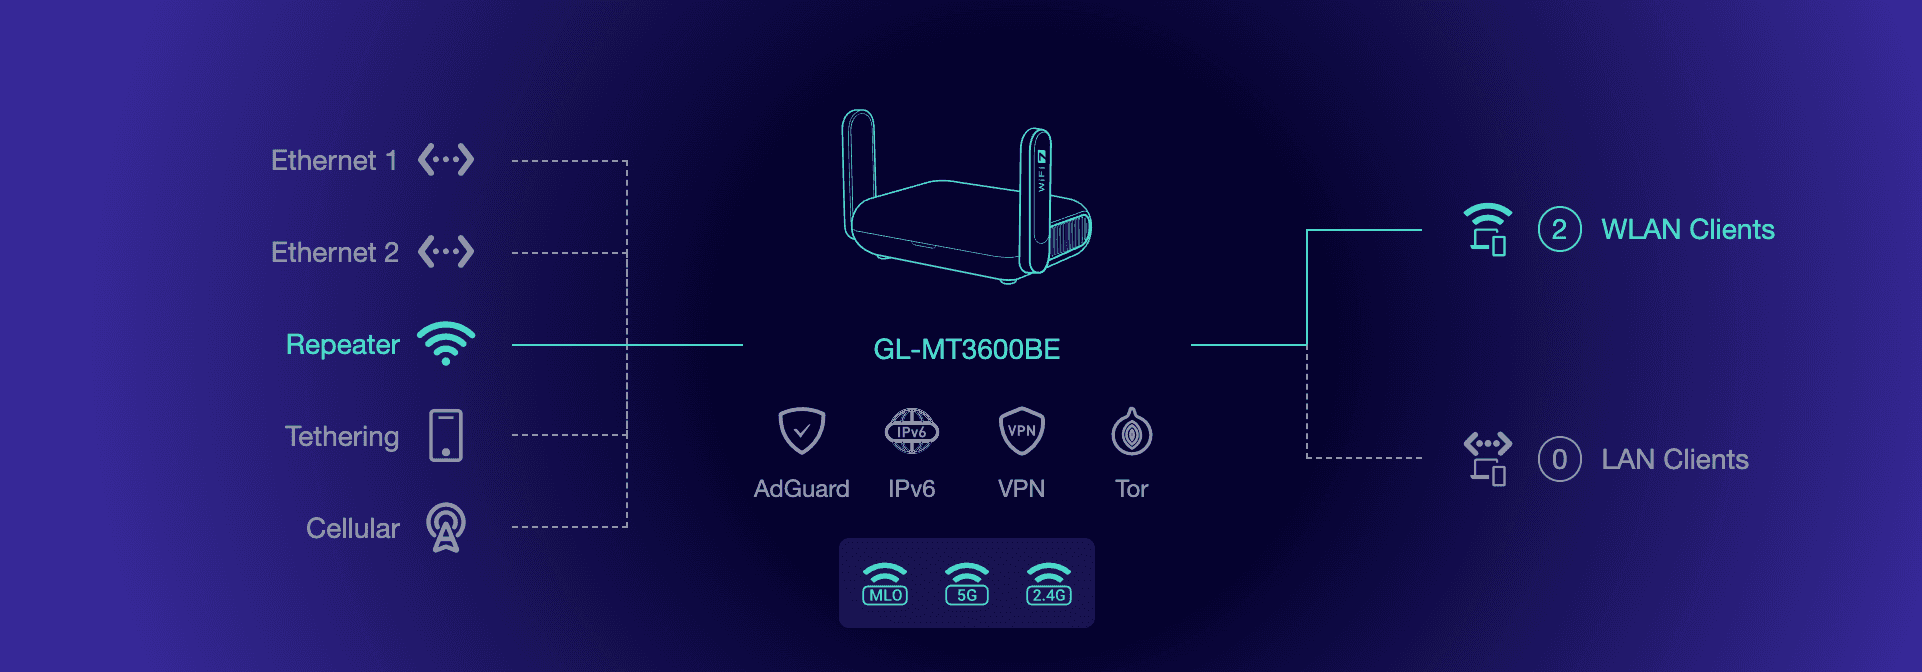
System topology
At a glance: the no-VPN path uses only the locally available internet connection; OpenVPN goes to a separate server-room endpoint; and WireGuard reaches the remote MikroTik, which has two separate internet uplinks from ONE and Telekom.
The three operating modes
The GL.iNet uses whichever local internet connection is currently available. This can be hotel or apartment Wi-Fi, Ethernet, or another available connection. In this mode, traffic reaches the internet directly without a VPN.
The second path is a separate OpenVPN tunnel terminating on a dedicated Linux server in a server-room environment with a fixed public IP address. The local internet connection only carries the encrypted tunnel.
The third path reaches a remote MikroTik router over WireGuard. Behind the MikroTik are two separate residential internet connections, ONE and Telekom, configured for failover.
Local internet
The GL.iNet can join an existing Wi-Fi network as a repeater, while Ethernet can also be used. Without a VPN, devices simply use that connection directly. The private SSID and internal network can remain unchanged, so laptops and phones do not need to be reconfigured at every location.
Two separate VPNs
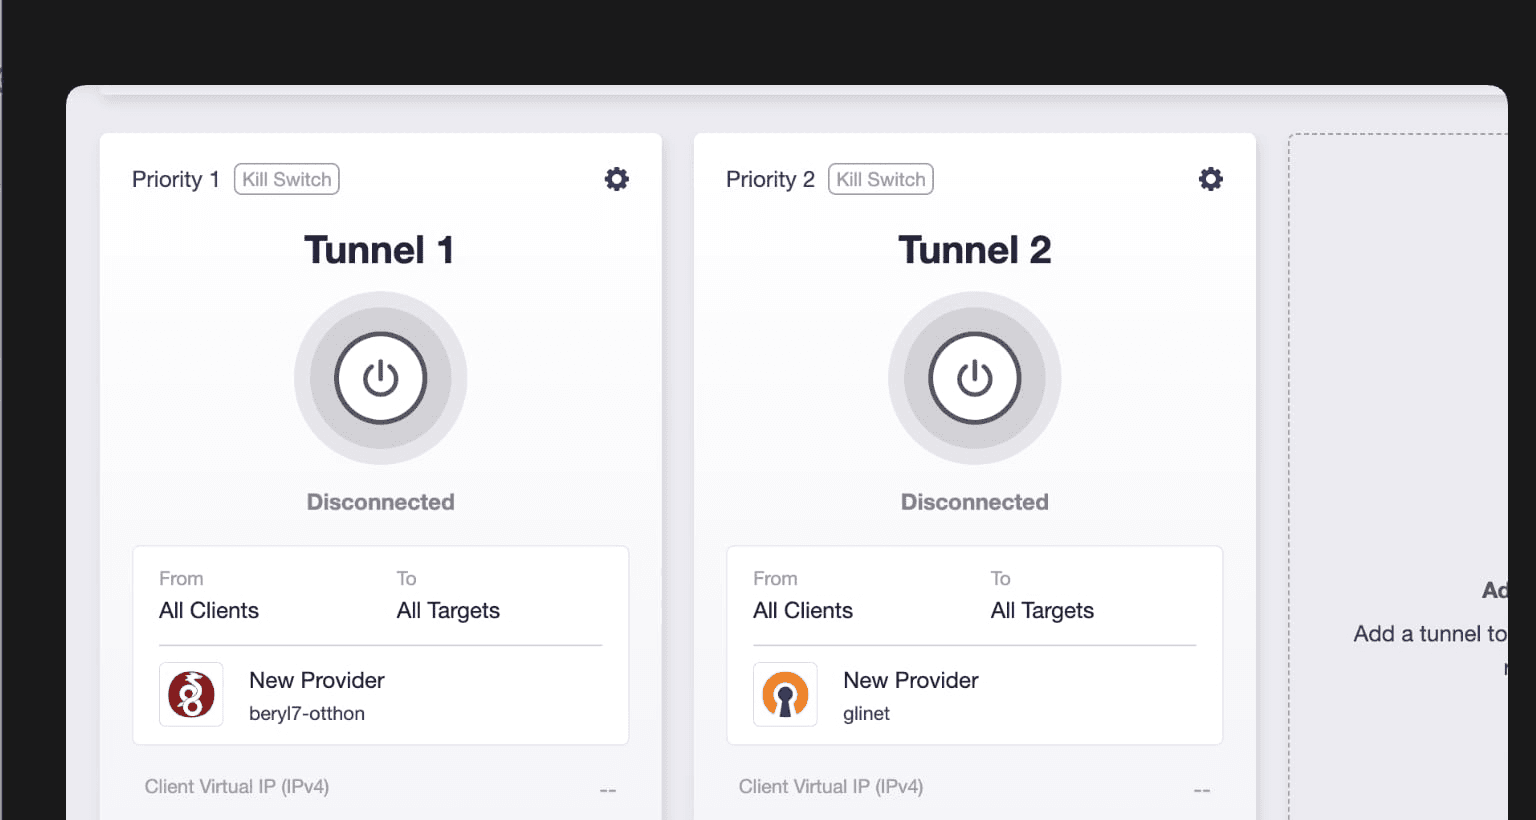
OpenVPN terminates on a separate server-room Linux server with a fixed IP address. WireGuard, by contrast, connects to the remote MikroTik. The two tunnels therefore serve different purposes and use different underlying infrastructure.
The physical side switch can quickly enable or disable WireGuard, while OpenVPN can be started manually from the VPN Dashboard when needed.
WireGuard endpoint
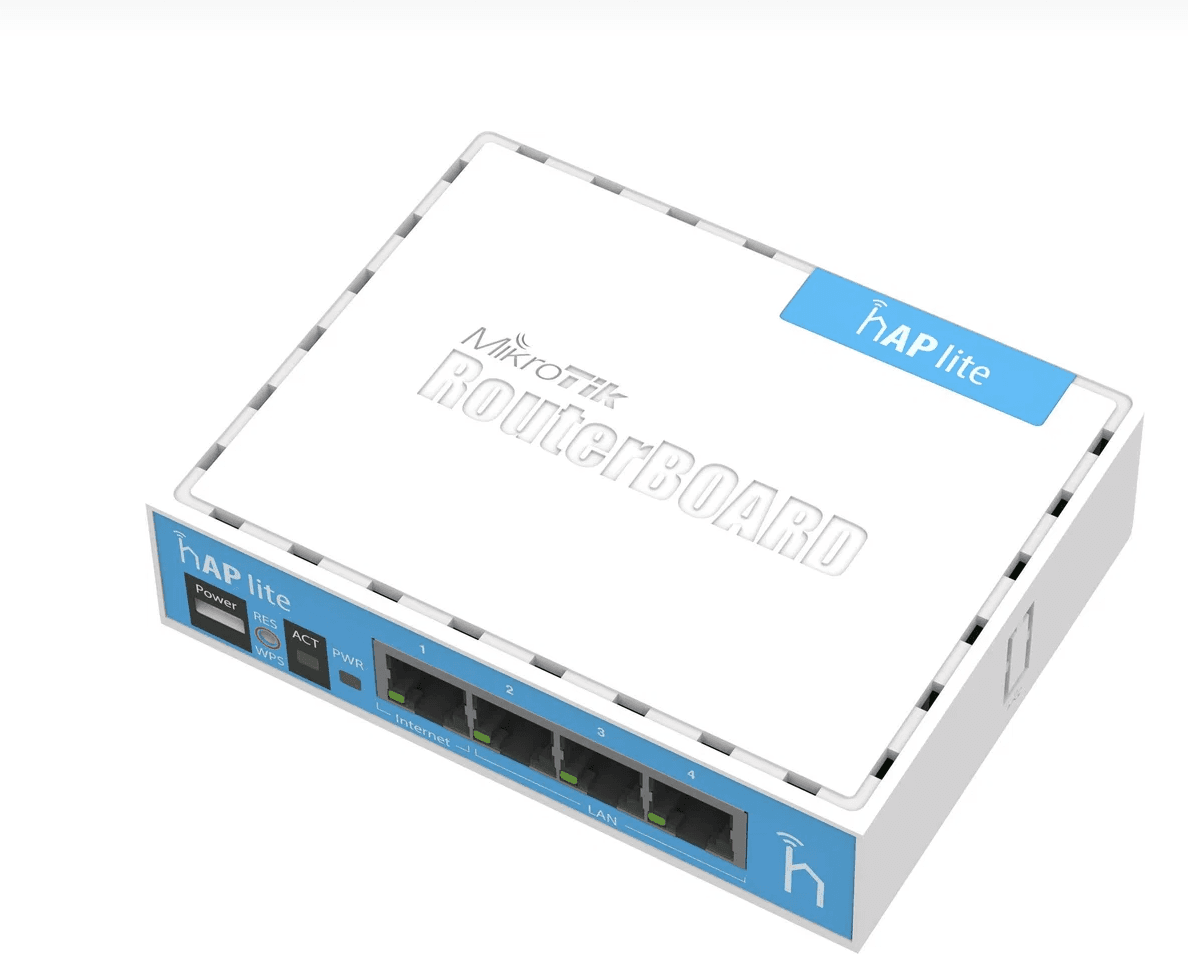
The WireGuard tunnel leads to a MikroTik hAP lite RouterBOARD. The MikroTik manages two separate residential internet connections: ONE and Telekom. The two WAN links operate in failover mode, so if one provider fails, the other can continue carrying the remote internet exit.
Why we built it
Laptops, phones and other devices do not need to know which hotel Wi-Fi, VPN or remote internet connection is currently in use. They always connect to the same private GL.iNet network, while the exit strategy is selected on the router.
The project combines several network solutions that we also deploy as standalone services.